
Clear the validation queue without lowering the bar.
gravityAI turns your models, vendor AI, and workflows into governed components deployed inside your own cloud. Each one carries its risk tier, its documentation, and lineage back to the data and version behind it. Validation opens a complete file, and oversight scales with real exposure.
Book a 30-minute diagnostic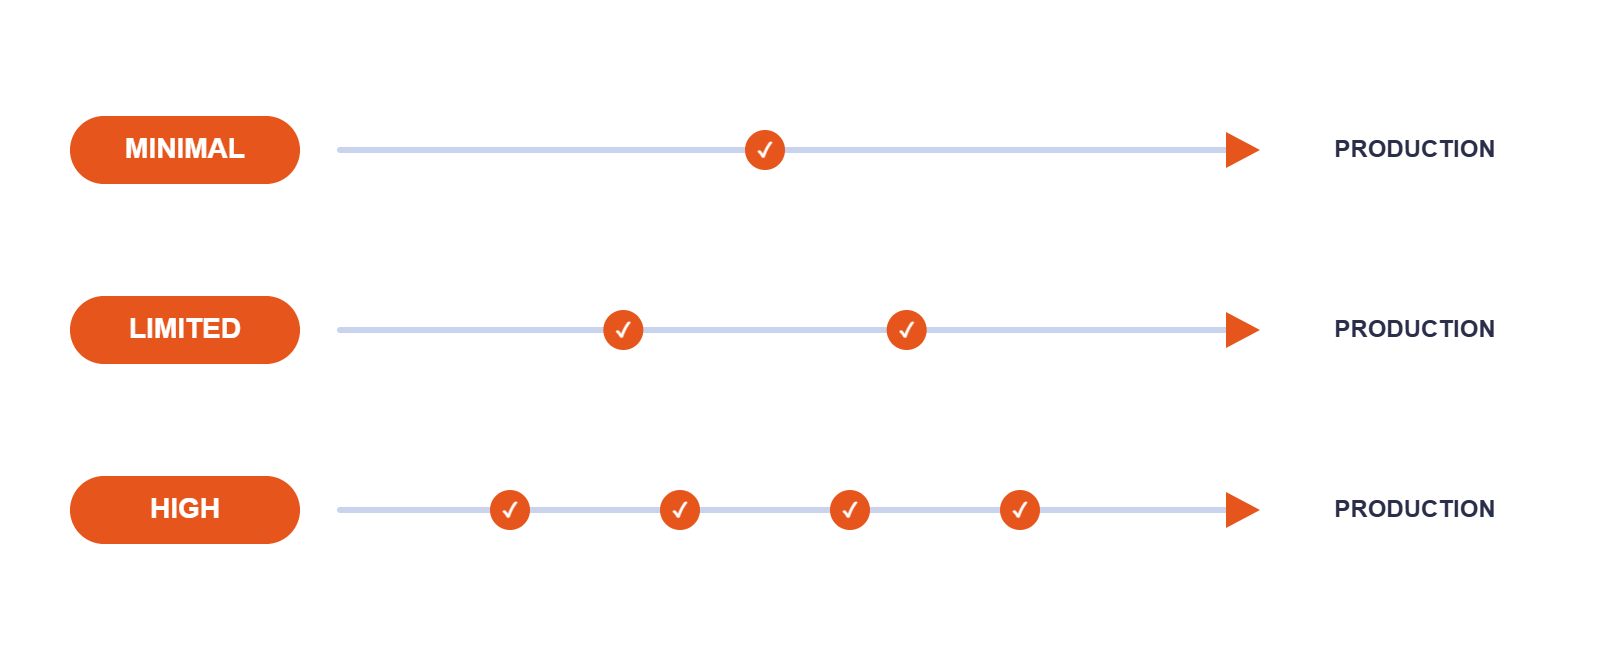
Three ways a good framework becomes the bottleneck
Banks have model governance. It was built for models that change once a year.
Governance is a property of the artifact
gravityAI is an AI toolbox and governance platform for regulated firms. Models, data connectors, vendor AI, and agentic workflows become governed microservices, deployed inside your own cloud.
Risk tier, documentation, ownership, access, change history, and lineage travel with the component from the moment it is deployed. Using the platform produces a documented artifact every time, by construction.
That changes what validation receives. Instead of chasing a developer for assumptions and a data dictionary, the reviewer opens a package the platform assembled while the work was being done. Your framework stays exactly as it is. The evidence arrives earlier.
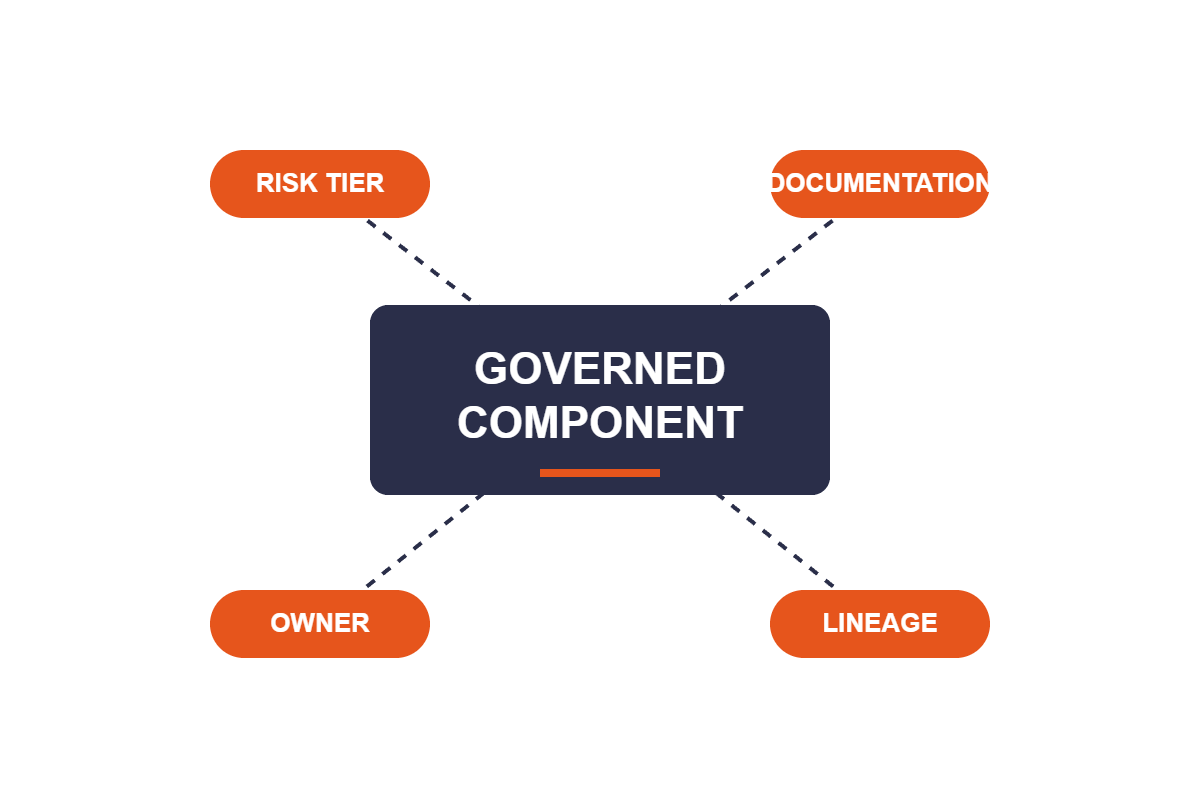
What governed actually means
| Control | How it works | Why it matters |
|---|---|---|
| Inventory | Every model, connector, vendor AI, and workflow registered as a deployed component | The inventory covers the tools nobody thought to call a model |
| Risk tiering | A risk level assigned to each component at deploy time | Proportionate review becomes the default path rather than an exception someone has to argue for |
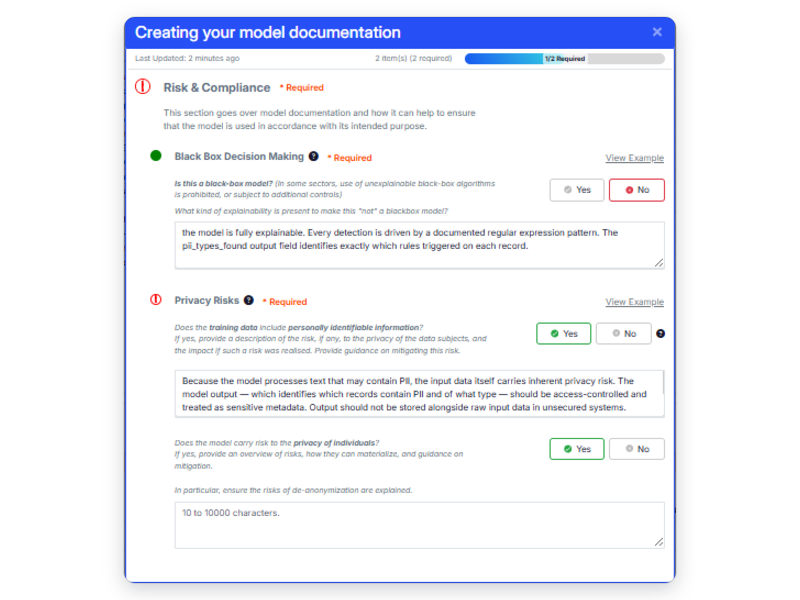
| Documentation | Business context, implementation detail, and risk assessment generated alongside the artifact | Validation opens a complete file on day one |
| Change control | Versioning, rollback, and a recorded history of what changed and when | Revalidation triggers fire on evidence rather than on a calendar |
| Lineage | Each output traces to the component, data source, and version that produced it | A specific decision can be reconstructed for an examiner, an auditor, or a customer |
| Access control | Role-based access to components and the data beneath them | Line-of-business and customer data boundaries hold while discovery stays open |
| Deployment location | Your cloud, on-prem, or air-gapped | Customer data stays inside your perimeter |
Governance applied to the artifact is a control. Governance applied to a process is a policy. Only one of them survives contact with a deadline.
From one team's model to a governed enterprise component
Bring what you already have. Core banking and loan origination systems, document stores, customer and transaction data, vendor AI and fintech partner APIs, and your own LLM provider, connected once and available to everyone cleared for them.
• Upload existing Python and risk models
• API connectors for core systems and third-party data
• Your LLM provider, your keys, your contract
• Runs in your VPC, on-prem, or air-gapped
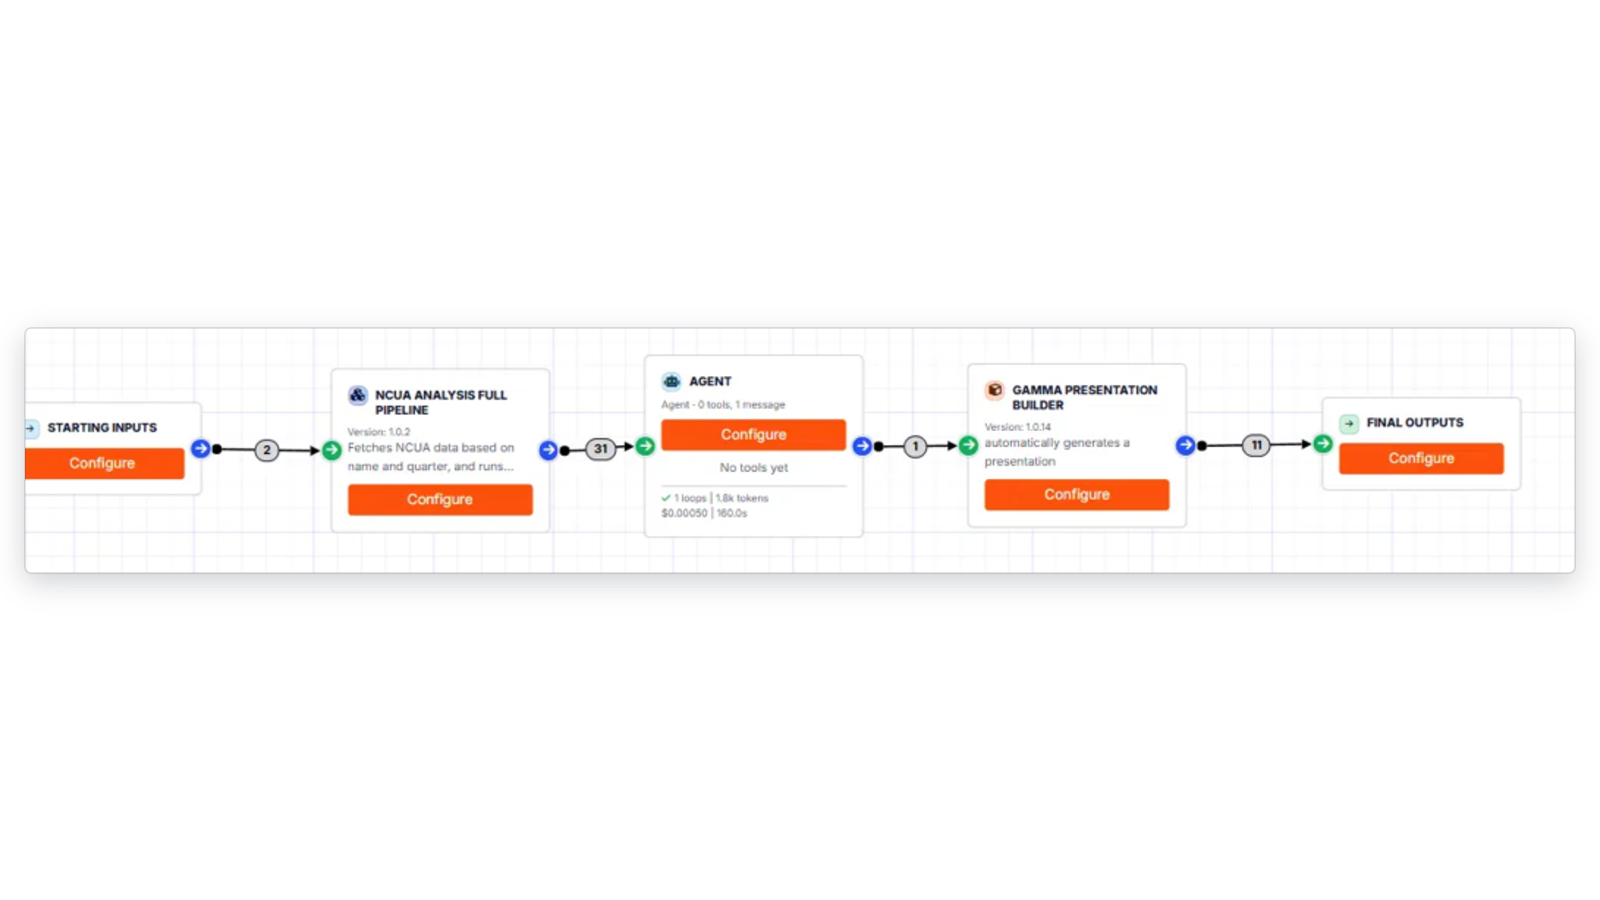
Assemble components into decision workflows. Lending and operations teams build in the no-code canvas. Quants and data scientists drop into the API and extend the same components in code. Same building blocks, two front doors.
• Drag-and-drop agentic workflow builder
• Full API and code path for technical users
• Chain models, connectors, and LLM steps
• Human-in-the-loop checkpoints where a decision affects a customer
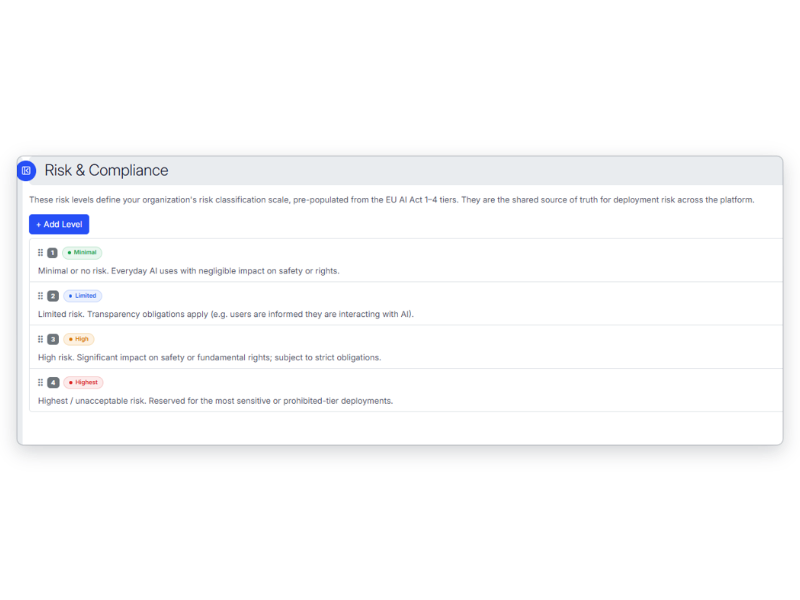
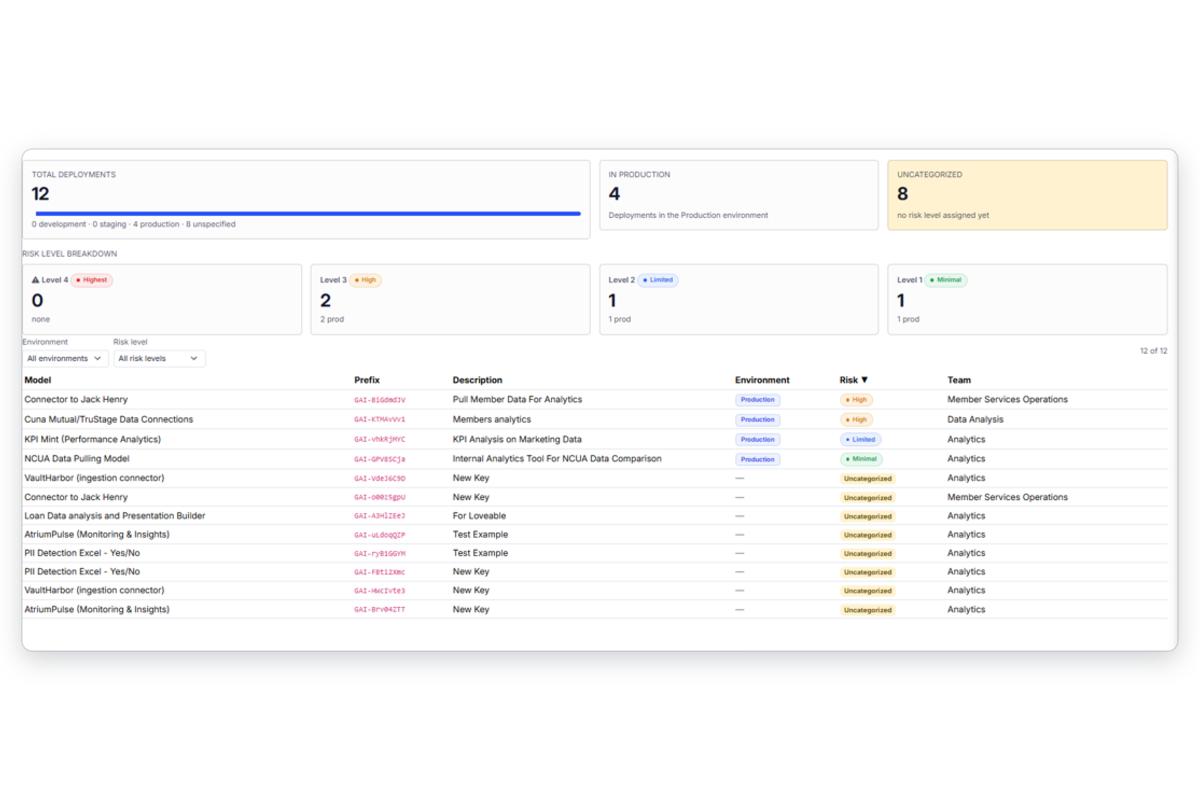
Every component carries a risk level and its own documentation, generated as it is built. Every deployment across every line of business shows up in one dashboard, including vendor AI and the components nobody registered.
• Risk tier assigned per component
• Business, implementation, and risk documentation generated with the artifact
• Single dashboard across every deployment and line of business
• Access control, change history, audit trail, and lineage by default
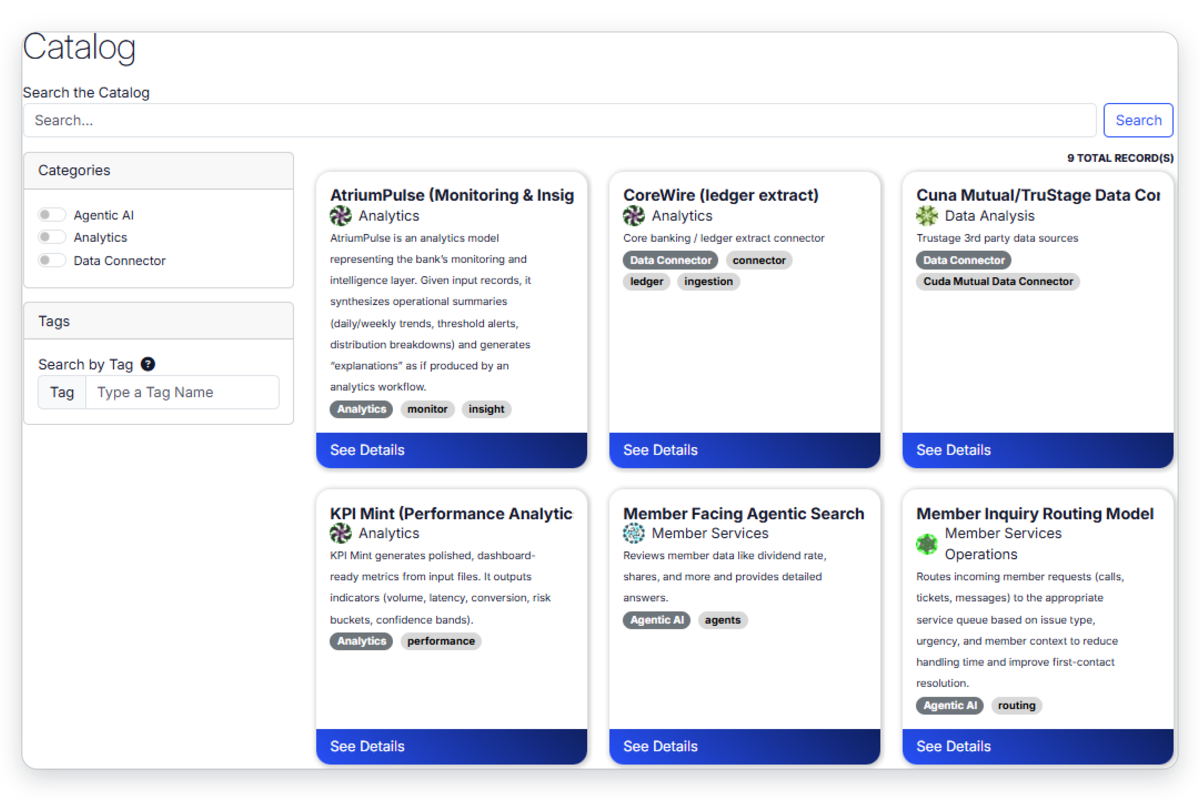
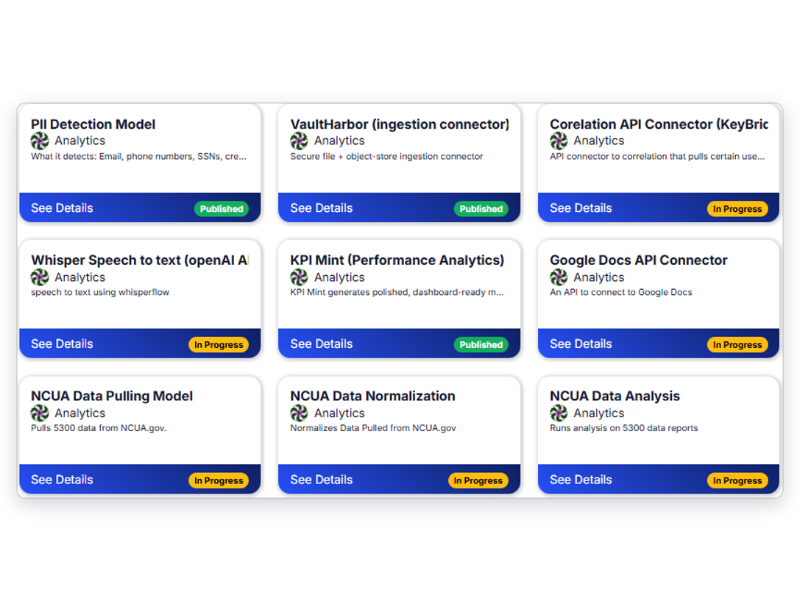
Publish to an internal catalog. The commercial team's document extraction component becomes the mortgage team's starting point, with its assumptions, documentation, and validation history attached. The second line of business inherits the evidence along with the code.
• Internal catalog of models, workflows, and connectors
• Fork and adapt an existing component
• Usage attributed to the creator
• Versioning and rollback
One platform, three teams with different definitions of done
The model risk and validation lead
Every deployed model, in-house and vendor, in one view
Risk tiering applied at deploy time
Documentation and lineage that exist because the platform made them
Change history that shows what moved and when
The data science or analytics lead
Publish work as a governed service other teams can use
Find prior work before starting from scratch
A defined path to production that runs without a ticket queue
Your code, your libraries, your standards
The lending or operations owner
Compose workflows without writing code
Adapt a component another line of business already cleared
Live data from core systems you already trust
Keep a human in the loop where the decision affects a customer
Where banks start
Patterns banking teams build with governed components.
Build it, bolt it on, or deploy it governed
| Feature | Build in-house | Workflow tool plus governance overlay | gravityAI |
|---|---|---|---|
| Governance attached to the deployed artifact | — | — | ✓ |
| Risk tier assigned before anything reaches production | — | — | ✓ |
| Documentation generated with the model | — | — | ✓ |
| Vendor and third-party AI in the same inventory | — | — | ✓ |
| Change history and rollback per component | — | ✓ | ✓ |
| Runs inside your own cloud | ✓ | — | ✓ |
| Live without a multi-quarter build | — | ✓ | ✓ |
Questions we get from banks
Evidence, earlier, and a tier that means something operationally. Your framework and your validation standards stay as they are. What changes is that every component arrives with its documentation, its risk tier, its change history, and its lineage already attached, and that low-risk components stop consuming the same review capacity as high-risk ones.
It is designed to feed an existing framework rather than replace one. Documentation covers business context, implementation, and risk. Change control and versioning are recorded per component, and lineage runs from an output back to the data and version that produced it.
They register as governed components alongside your own, with a risk tier, an owner, and access controls, which puts third-party AI in the same inventory as everything you built.
Yes. gravityAI runs in your secure cloud, on-premise, or air-gapped. Models and customer data stay inside your perimeter, and deployments inherit your existing access controls.
No. It sits on top of them. gravityAI connects to the core, the warehouse, and the vendor APIs you already have, and makes what gets built on them governable and reusable.
No. You connect your own LLM provider under your own contract, and your data and models stay in your environment.